
Q&A with Jasie Fon, Regional Vice President (RVP) of Asia, Ping Identity, on how AI-driven identity and access management (IAM) is reshaping cybersecurity and compliance across Southeast Asia’s interconnected supply chains.
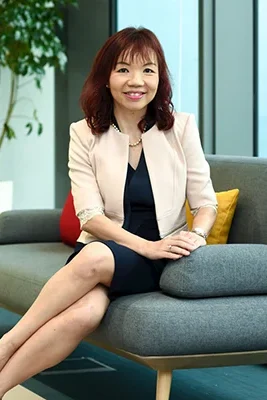
1. Ping Identity recently launched its services on AWS Singapore – marking a major milestone for its operations in Southeast Asia. How does this local deployment enhance IAM capabilities for regulated industries in Southeast Asia?
This is a major milestone for us and for the region.
With Ping Identity now available on AWS Singapore, customers across Southeast Asia, particularly those in regulated industries like banking, healthcare and government, gain access to a highly secure, Singapore-hosted identity infrastructure.
Data residency, low-latency access and regulatory compliance are non-negotiable in these sectors.
Many of our customers are under legal obligations to keep personal data within national borders. Hosting on AWS Singapore enables them to meet these requirements while still leveraging the flexibility and scalability of the cloud.
When identity services are hosted closer to the user base, login and verification processes become faster, more reliable and more secure.
Many organisations in ASEAN are moving to multi-cloud or hybrid environments. Our local deployment ensures they can do so while meeting both business and regulatory expectations.
2. With 54% of organisations experiencing third-party breaches, how is Ping Identity using AI to transform external access into a strategic defence layer?
Third-party access is no longer a fringe concern but one of the largest and most exploited attack vectors in today’s digital enterprise. Whether it’s a vendor accessing a partner portal or a contractor using internal tools, each third-party relationship introduces risk.
Ping Identity uses AI and Machine Learning to continuously monitor behaviour patterns, such as login frequency, IP addresses, device types and keystroke dynamics across all users, including external ones.
This allows us to build a dynamic risk posture. If an external user suddenly logs in from an unfamiliar location or attempts to access systems they don’t normally use, the system can trigger adaptive policies: step-up authentication, session termination or even access revocation.”
We’re no longer relying on static roles or credentials. Instead, we’re making real-time access decisions based on context, behaviour and AI-derived risk signals. This turns identity into a continuously monitored layer of defence.
3. Can you explain how Identity Visibility and Intelligence Platforms (IVIP) differ from traditional IAM tools – and why they’re critical for today’s supply chain ecosystems?
Traditional IAM tools are largely reactive – they manage user identities, authenticate access and enforce policies based on pre-defined roles. However, they often operate in silos and lack real-time intelligence or holistic visibility.
An Identity Visibility and Intelligence Platform (IVIP), on the other hand, is proactive, unified and analytics driven. It collects identity signals from across your entire IT environment – cloud apps, legacy systems, mobile endpoints, third-party connections – and correlates them to detect anomalies, assess risks and inform adaptive policies.
This is especially critical in supply chain ecosystems, where identity data is fragmented across multiple organisations, platforms and jurisdictions. An IVIP gives you a unified view of who is accessing what, when and why – and whether that access represents a potential threat.
4. How are Southeast Asian enterprises shifting from perimeter-based security to identity-first architectures, especially in B2B environments?
The perimeter is dissolving. In response, many enterprises are moving to identity-first architectures, where identity becomes the new perimeter.
In B2B environments, this shift is particularly pronounced, organisations need to provide secure access to partners, vendors and affiliates, often with federated identities and without traditional network-based controls. That’s where Ping Identity comes in.
We enable organisations to adopt a zero-trust approach to identity. That means no implicit trust based on network location or device type. Every access request is continuously evaluated based on user identity, behaviour, device health and risk context.
5. What role does Ping Identity play in helping organisations meet evolving compliance standards like PDPA, MAS TRM and regional data residency laws?
Compliance is a moving target and in Southeast Asia, it’s moving fast. Our platform supports in-region deployment, ensuring sensitive identity data remains within national borders while enabling global scalability. This, coupled with comprehensive audit and consent management capabilities, makes it easier to meet compliance standards.
Ultimately, Ping Identity helps enterprises turn compliance into a competitive advantage, building trust with customers, partners and regulators while future-proofing their identity infrastructure.
6. How does AI-powered IAM improve operational efficiency for enterprises juggling multiple identity systems across cloud and on-prem environments?
The typical enterprise today is juggling four to six identity systems. This fragmentation creates security gaps, inefficiencies and administrative overhead.
Ping Identity uses AI tools to orchestrate identity workflows across these silos intelligently. We automate identity lifecycle management, threat detection and policy enforcement. Helix will embed AI into all our identity operations to improve productivity and streamline processes.
“This will lead to measurable improvements in operational agility, especially for sectors like finance and government that require both cloud-native capabilities and infrastructure control. We recently announced our dedicated framework to secure AI agents with the same rigour as human identities.
7. Looking ahead, what innovations in IAM, such as digital credentials or passwordless authentication, are gaining traction in Asia’s most regulated sectors?
“We’re seeing strong momentum around two innovations: passwordless authentication and verifiable digital credentials (VDCs). Driven by FIDO2 standards and biometric authentication, passwordless authentication eliminates reliance on passwords, which is still the root cause of over 80% of breaches.”
“Ping Identity is engaging with governments, regulators and enterprises across ASEAN to promote these technologies,they align well with the region’s push for trusted digital ecosystems – think Singapore’s National Digital Identity (NDI) or Indonesia’s e-KTP integration.”
“These innovations represent a shift toward identity ecosystems that are secure, interoperable and privacy-preserving. For enterprises juggling compliance with PDPA, MAS TRM and other regional mandates, passwordless and verifiable credential-based authentication offer a scalable path to both security resilience and regulatory alignment.
“As regulatory standards evolve and cyber threats intensify, these technologies will play a pivotal role in helping organisations stay ahead of both compliance and credential-based attacks, while delivering a frictionless experience to users across sectors.”
“The future of IAM in Asia is decentralised, intelligent and user-centric – Ping Identity is committed to shaping that future responsibly.”

